From Knowledge to Capability: Applying Methods with Control
For enterprise leaders and practitioners, a six-step approach to turning approved knowledge into usable capability while preserving evidence, decision authority and control.
On this page
- Reading a method is not the same as being able to use it
- Preserve the source, define the authority
- Six steps from knowledge to governed capability
- Establish the task and ground the answer
- Separate reasoning from permission
- Check the consequence and retain the record
- An illustrative example: applying a market diagnostic
- Test the cases that should not proceed
- Choose capability, not maximum autonomy
Knowledge becomes capability when a method can be selected, applied, evaluated and governed for a defined task without losing the source that gives it legitimacy. Retrieving or summarising that method is only the beginning. The enterprise challenge is to make it usable while preserving evidence, decision authority and control over what happens next.
Reading a method is not the same as being able to use it#
An AI-generated answer can sound convincing while relying on the wrong source, incomplete context or an incorrect policy assumption. Fluency does not establish that a method applies, that its interpretation is sound or that anyone has permission to act on it.
The useful question is not simply, “Can the system read our knowledge?” It is, “Can people and systems apply an approved method within its limits, explain the result and stop when the proposed action exceeds their authority?”
That distinction matters whenever an answer influences a business commitment. Operational capability requires more than an explanation: it requires a dependable connection between knowledge, judgement and permitted action.
Preserve the source, define the authority#
A method’s provenance is its origin and basis for legitimate use: where it came from, which version applies and why it is appropriate for the task. Converting it into an automated workflow should not erase those details.
A retrieved statement remains evidence, not automatically the current organisational rule. Where sources conflict, the conflict should be visible. A confident synthesis is not a substitute for establishing which source has precedence.
Three responsibilities need to remain distinct:
- Interpretation: what does the evidence suggest?
- Decision authority: who may approve the resulting business commitment?
- Execution: what may be changed, through which controlled mechanism?
Putting all three into one language-model instruction can obscure which control permitted or prevented an action. Clear ownership is needed for input quality, source precedence, decision scope, execution checks and record retention.
The central risk is losing a method’s provenance as it moves into automation. A demonstration with complete information and an authorised request may not reveal that failure.
Six steps from knowledge to governed capability#
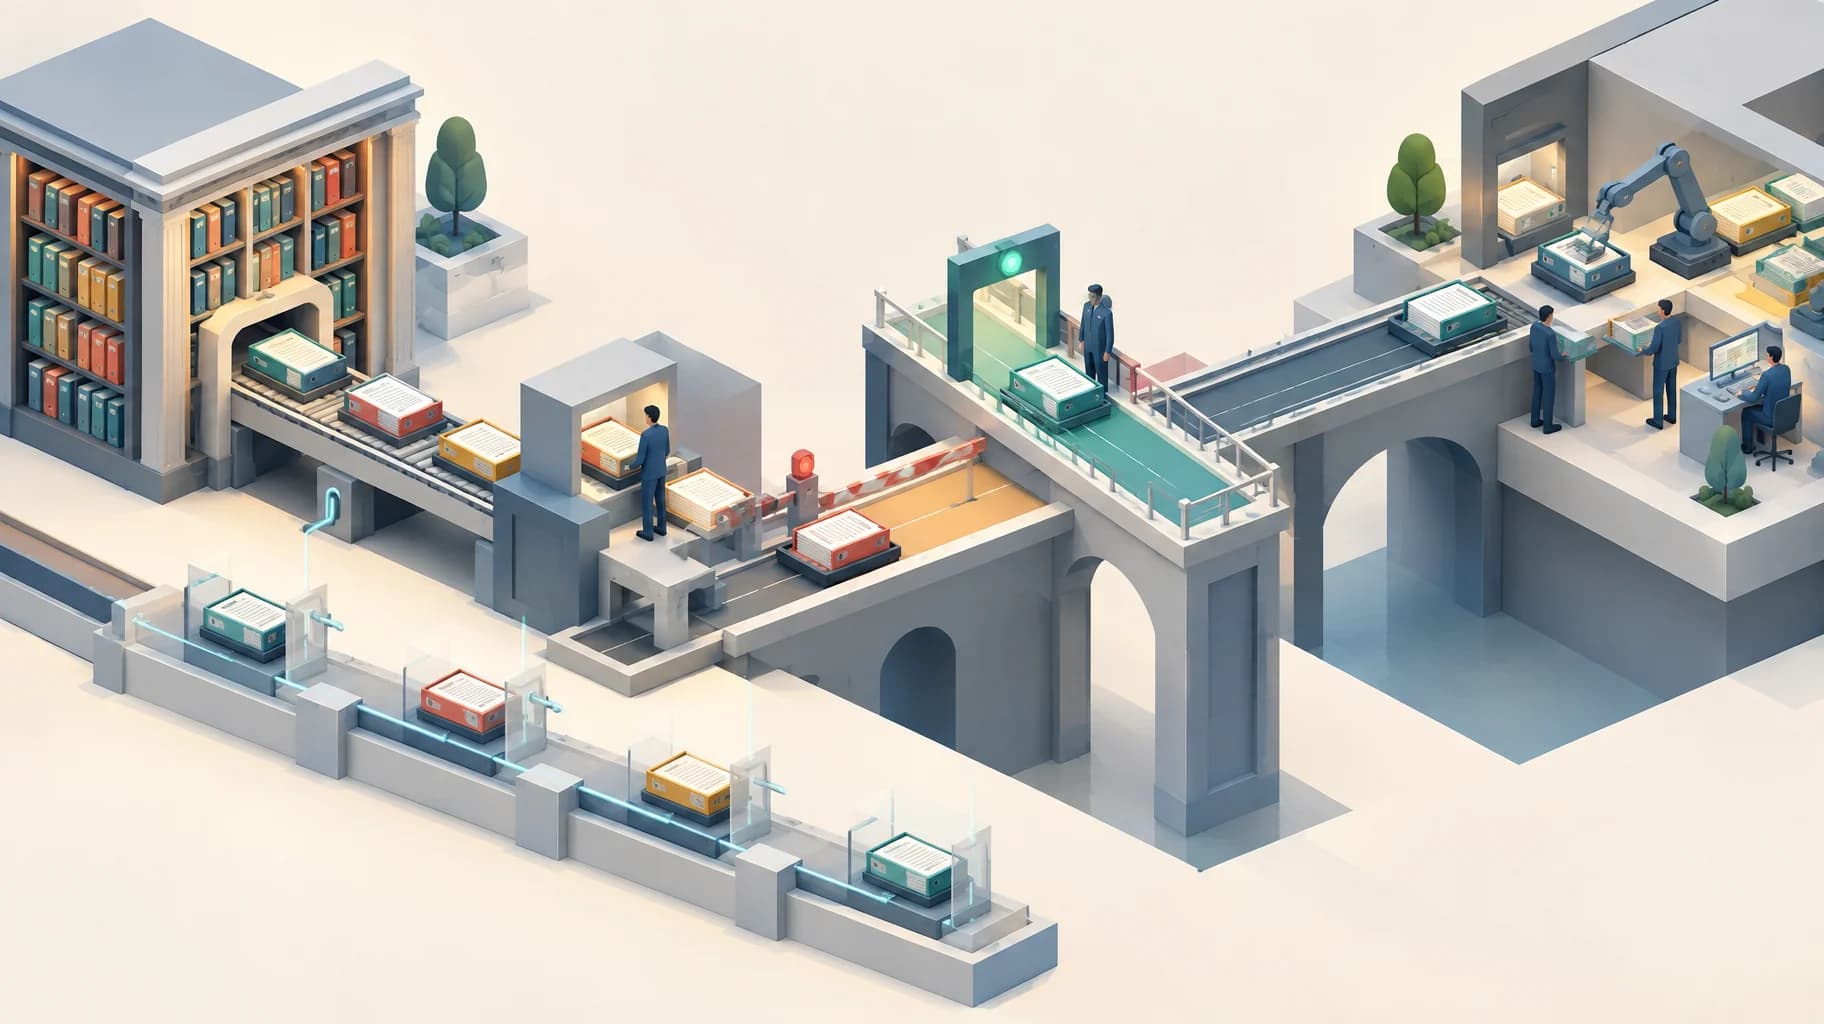
This operating model treats knowledge use as a governed process, rather than a single request for an answer.
Establish the task and ground the answer#
1. Establish the legitimate question. Define the business decision, the person or role asking, the intended outcome and the permitted data domain. Clarify whether the task is to explain, recommend, approve or execute: these are different responsibilities.
2. Ground the answer. Identify the approved sources and the versions relevant to the task. Check their currency, missing information and conflicts before applying the method. If the evidence cannot support a conclusion, state that limitation rather than filling the gap with plausible language.
Separate reasoning from permission#
3. Separate interpretation from enforcement. Reasoning can propose an action, but that proposal should not grant access or business authority. Access controls, resource limits and execution policies need controlled enforcement mechanisms, not just a model’s interpretation of what is allowed.
4. Use the right depth of work. Match the reasoning effort to the problem and its consequences. Specialised reasoning may help with complexity, but it also brings latency, configuration demands, additional failure points and review needs. More elaborate reasoning does not guarantee a better answer.
Before expanding the work, establish which tools may be used, what budget applies and whether conclusions may be returned to shared context.
Check the consequence and retain the record#
5. Inspect the proposed consequence. Before an action changes the business, check its target, the requesting role, any amount involved, its scope, its owner and the exception path. If the proposal exceeds an authority threshold or depends on unresolved evidence, human review may be the correct result.
6. Retain the meaningful trail. Keep enough information for another qualified person to reconstruct the decision: the starting context, sources, interpretation, authority check and outcome. Record what was blocked or escalated as well as what was executed.
The aim is a useful decision record, not uncontrolled duplication of sensitive information. Retention and access requirements still apply.
An illustrative example: applying a market diagnostic#
Consider a proprietary market diagnostic used to guide the next research question. This is an illustrative scenario, not evidence of a current Dainin deployment, benchmark result or security certification.
The process begins with the business objective and the approved sources for the diagnostic. The method is then applied to produce an interpretation that can be inspected alongside its evidence.
If approved sources contradict one another, the interpretation should expose that disagreement. It should not quietly choose whichever evidence produces the neatest answer.
The next boundary concerns authority. A recommendation for further research is not automatically permission to initiate the next workflow. Where evidence remains unresolved or the proposed step exceeds permitted scope, the result should go to human review.
Only an authorised action should proceed. The useful output is therefore not merely a diagnostic conclusion, but an auditable interpretation that records whether the next step was approved, blocked or escalated.
Test the cases that should not proceed#
A normal case shows whether a method can work under expected conditions. It does not establish whether the system respects its boundaries.
A practical verification protocol should include six steps:
- Define the allowed result. State what the method may conclude or change, and which outcomes are unacceptable.
- Fix the input and source snapshot. Preserve the starting conditions so the result can be checked against the same evidence.
- Run a normal case. Test an authorised request with sufficient information and an expected permitted outcome.
- Run a contradictory case. Introduce conflicting evidence and inspect whether uncertainty is exposed rather than concealed.
- Run an unauthorised case. Test whether an otherwise plausible request is blocked or escalated when permission is absent.
- Review the record. Ask another qualified person to reconstruct what happened and why.
Capture the results in a method applicability and test case register. For each case, record the starting context, permitted result, actual result and whether an action was blocked, escalated or executed.
Include partial completion and failures, not just clean successes. A workflow that completes one stage and fails at another still needs a record of what changed and what remains unresolved.
A refusal or human escalation can be a successful outcome; a fluent but unauthorised action is not.
Repeat testing when models, tools, policies or source sets change. Earlier results describe the conditions tested, not every future configuration.
Choose capability, not maximum autonomy#
Codifying a method can support reuse, but it does not remove the need for expert judgement in edge cases. The appropriate degree of autonomy depends on the task, the quality of the evidence and the consequences of error.
Extra reasoning and verification also have costs, including latency, review effort and maintenance requirements. Weigh those costs against the cost of errors rather than omitting them from the business case.
The practical standard is observable behaviour. Can the method be applied within its limits? Can an unauthorised action be stopped? Can another qualified person reconstruct the outcome?
Start with one approved method. Define its permitted use, authoritative sources and decision owner. Test a normal case, a contradictory case and an unauthorised case. Record what happened and whether another qualified person can reconstruct it. That is a concrete test of whether knowledge has become governed capability, rather than simply a plausible answer.