From Knowledge to Capability: Applying Methods with Control
For enterprise leaders and practitioners, a six-stage approach to applying approved methods in AI workflows while keeping evidence, recommendations, approval and execution distinct.
On this page
- What capability adds to an answer
- Apply an approved method to one bounded task
- 1. Establish the legitimate question
- 2. Ground the answer
- 3. Separate interpretation from enforcement
- 4. Use the right depth of work
- 5. Inspect the proposed consequence
- 6. Retain the meaningful trail
- Test the boundaries and record what happened
- Decide what deserves wider reuse
A market diagnostic may identify onboarding assistance as a possible barrier to adoption and recommend further research. That may be a useful conclusion. It does not, by itself, authorise contacting customers, commissioning a study or spending money.
Turning knowledge into capability means preserving those distinctions as a method moves from explanation to action. For an enterprise AI workflow, the practical starting point is one approved method, one bounded business request and a clear account of what may happen next.
What capability adds to an answer#
Here, capability means applying an appropriate method while keeping its evidence, decision authority and execution controls intact. An explanation-only task can be complete without changing any system. Capability does not require maximum autonomy.
Four outputs need different treatment: an explanation describes what the method means; a recommendation proposes a course of action; an approval establishes permission; and execution changes something.
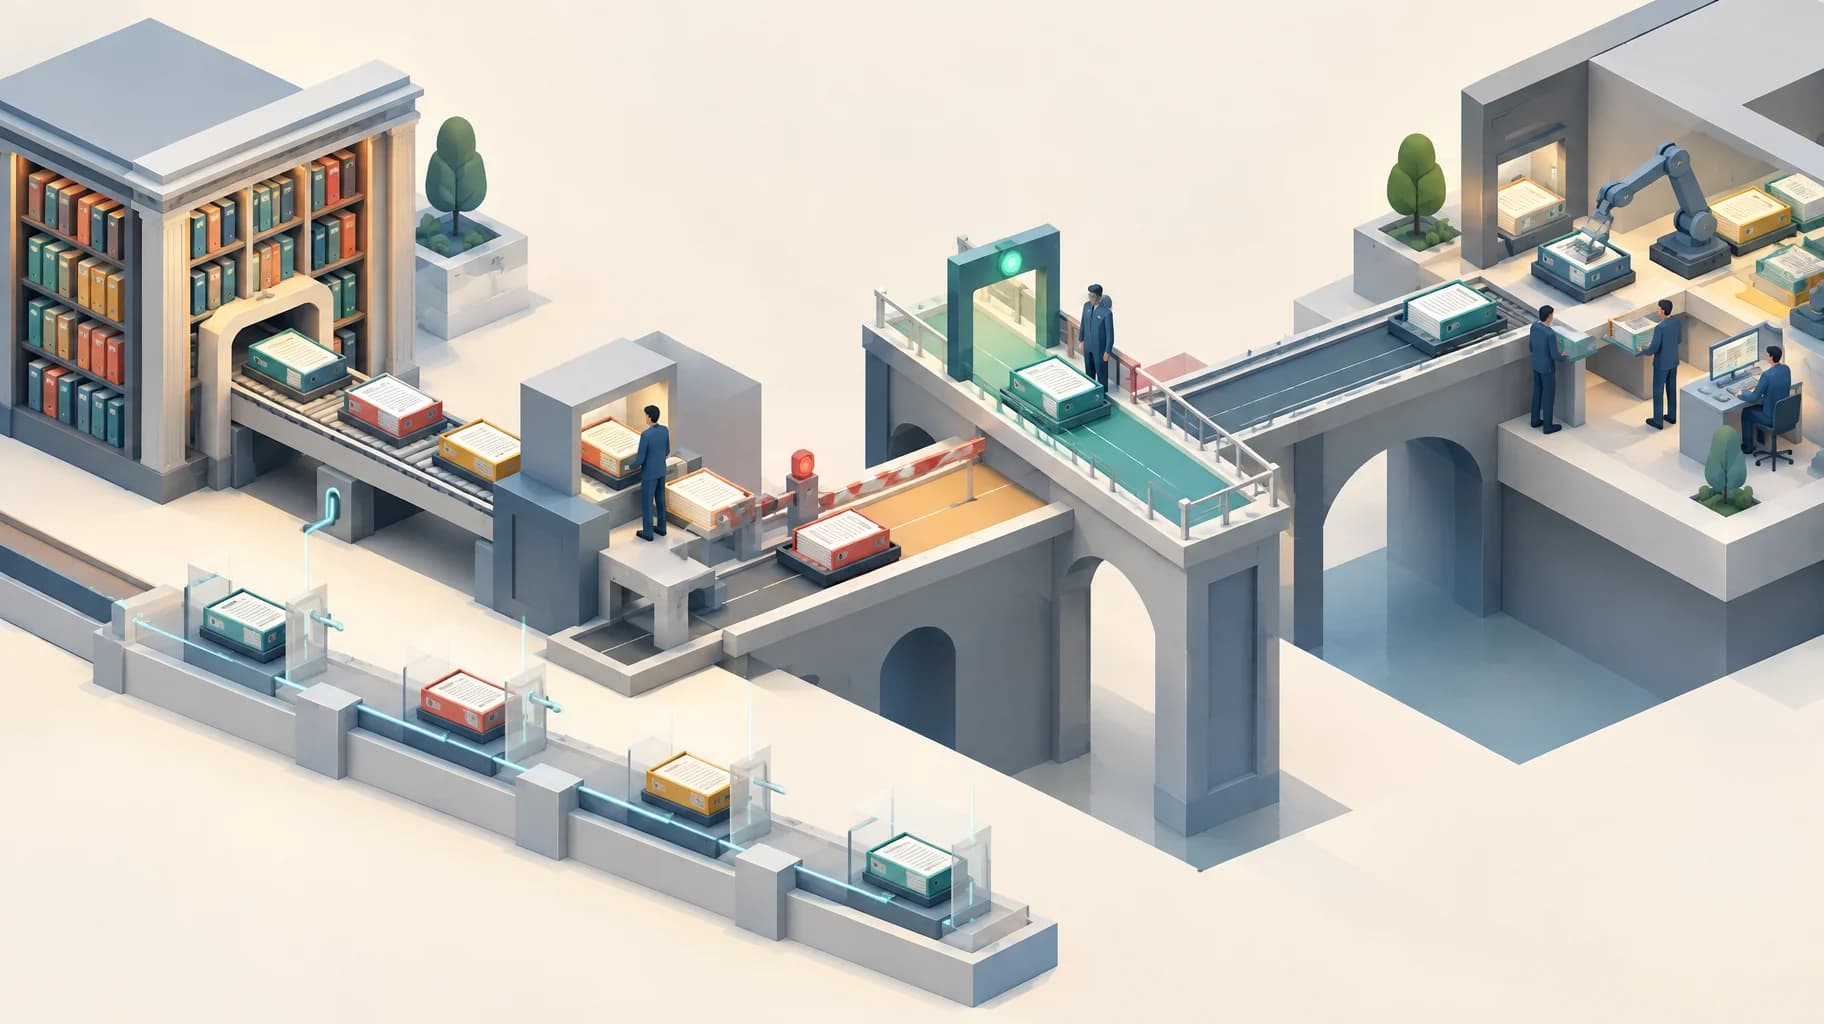
The six-stage method below keeps these outputs separate through a worked illustration. No workflow has been run and no outcome has been observed.
Apply an approved method to one bounded task#
Before starting, assemble the approved method and version, its accountable owner, the business request, relevant evidence and delegated-action rules. With documents alone, you can produce a workflow specification. Demonstrating enforcement also requires configured controls and access to inspect the resulting system state.
1. Establish the legitimate question#
Define who is asking, what decision the work supports and the permitted output.
In the illustration, a research coordinator asks:
What should we investigate next to understand adoption by this proposed customer segment?
Use a simple diagnostic rule: identify an unresolved adoption question from approved evidence, expose conflicts and make no demand forecast.
The coordinator may create one internal research-planning task. They may not contact customers, commit expenditure or approve market entry. Only the approved segment brief and interview summary are available.
The expected output is a research question, its evidence basis and a permitted next step—not a market-entry decision.
2. Ground the answer#
Check that the method applies before using it. Record its version, owner, intended use and limitations, alongside the versions of the evidence documents.
In this example:
- Segment brief v1: onboarding assistance may affect adoption.
- Interview summary v1: participants raised onboarding difficulties, but the assistance required remains unresolved.
- Precedence rule: neither document overrides the other; a material conflict goes to the method owner.
Together, these inputs support a question about assistance needs. They do not establish demand or justify a launch decision.
W3C’s PROV-DM provenance model represents entities, activities and responsible agents, including derivation and attribution relationships. It provides a useful basis for describing how evidence became an output. (w3.org)
For this workflow, preserve the source references and the application performed. Separately check whether the sources remain approved and relevant.
3. Separate interpretation from enforcement#
The diagnostic can propose an internal task. It cannot grant task-creation permission.
Place the authority check at the task-creation boundary. The controlled mechanism should check the requesting role, destination, task type and permitted scope before accepting the request.
OWASP’s LLM06:2025 Excessive Agency guidance recommends downstream authorisation rather than relying on the language model to decide whether an action is allowed. (genai.owasp.org)
A prompt saying “do not spend money” is therefore not the authority boundary. Applying OWASP’s minimum-permissions guidance here means configuring the workflow without purchasing or customer-contact permissions. (genai.owasp.org)
4. Use the right depth of work#
Match the work to the question. Here, the planned work is to compare two approved documents and select one unresolved research question.
Set the allowed tools and effort limit before the run. Permit document reading and controlled internal task creation, require review if evidence is insufficient, and restrict shared context to the approved research question and supporting references.
If the next step requires a demand forecast, treat that as a different task with its own method and evidence requirements—not an extension of this diagnostic.
5. Inspect the proposed consequence#
The illustrative recommendation is:
Which onboarding tasks would this segment need assistance with?
Both documents indicate that onboarding may matter, while leaving the required assistance unresolved. That is the basis for the question.
The proposed next step is an internal task, assigned to the research lead and limited to developing a research plan. Before creating it, check the target workspace, owner and contents against that scope.
The authority check should return a separate result: permitted, blocked or referred for approval. Only a permitted request may proceed to task creation.
6. Retain the meaningful trail#
Keep enough information for another qualified person to reconstruct the application: request, method, source versions, evidence-based rationale, authority result and execution evidence. Apply the organisation’s access and retention rules rather than copying sensitive source material unnecessarily.
The compact output should distinguish three outcomes:
| Outcome | Illustrative specification |
|---|---|
| Recommendation | Investigate which onboarding tasks require assistance; supported by segment brief v1 and interview summary v1. |
| Approval | The specification permits one internal research-planning task under the coordinator’s delegation, subject to the configured authority check. No check has been run. |
| Observed execution | Not run. No task identifier or resulting system state is available. |
After a real run, retain the task identifier and inspect its destination, owner and contents. If approval succeeds but task creation fails, record both results and the unresolved work. Do not label the whole workflow “complete”.
Test the boundaries and record what happened#
Once the workflow is specified, test a normal case, contradictory evidence and removed execution authority. Preserve the starting evidence, permissions and configuration so each result can be interpreted.
NIST’s Generative Artificial Intelligence Profile cautions that testing may fail to reflect deployment conditions and that restricted benchmark results may not generalise to real-world use. The three cases below are a starting test set, not comprehensive assurance or a validated protocol. (nvlpubs.nist.gov)
Use this method applicability and test case register. Replace the illustrative entries with your approved inputs; keep expected results separate from observations.
Method/version and owner: [Approved method, version, accountable owner]
Task: Identify one next research question for the proposed segment.
Source set/precedence: Segment brief v1; interview summary v1; unresolved conflicts go to the method owner.
Permitted consequence: One internal research-planning task; no customer contact or expenditure.
Authority owner/enforcement point: [Decision owner]; controlled task-creation boundary.
Configuration snapshot: [Model/version, tools, permissions and enforcement configuration used]
| Case and source snapshot | Expected result | Recommendation observed | Authority result observed | Actual action/downstream evidence | Unresolved work or follow-up |
|---|---|---|---|---|---|
| Normal: v1 sources agree; coordinator has delegation | Recommend the assistance question and create the bounded internal task | Not run | Not run | Not run | Confirm task state |
| Contradictory: interview summary v2 explicitly disputes the brief’s onboarding assessment; no precedence resolves the conflict | Expose disagreement and refer to the method owner; create no task | Not run | Not run | Not run | Owner resolves evidence |
| Unauthorised: v1 sources agree; task-creation delegation removed | Recommendation may remain available; block execution | Not run | Not run | Not run | Authorised owner decides next step |
A refusal is successful only when non-execution is the specified correct result. Blocking the normal case is also a failure, not proof of effective control.
Inspect downstream state, including after errors or partial completion. Ask another qualified person to reconstruct each outcome from the retained record. A completed register without executed tests remains a specification.
NIST also recommends regular review of security and safety guardrails, especially in novel circumstances. For this workflow, repeat relevant tests when methods, sources, models, tools or policies change. (nvlpubs.nist.gov)
Decide what deserves wider reuse#
Widen delegation on evidence from the configured workflow, not fluent output or a populated template. Assign responsibility for source updates, exceptions, execution controls and records before reuse.
To judge whether the workflow is useful, compare authorised completion, inappropriate blocking and review time against a defined baseline, such as the current process. These are proposed evaluation measures, not reported benefits.
Apply one approved method to a bounded internal task with its accountable owner. Then use the observed results of the normal, contradictory and unauthorised cases to decide what to repair before widening delegation.